 Written by
Marion City Council is preparing to review emergency legislation authorizing the City Auditor to immediately enter into a contract with Software Solutions Inc. (SSI) and Right Stuff Software. The ordinance appears on the August 17 agendas in rapid succession, first before the Information Systems Committee and then before the Finance Committee, with no forensic safeguards in place.
The New World software system is, by definition, compromised, and both financial and IT standards—as well as the law—demand that a full forensic IT audit is conducted either before or during this transition.
“Item 1. Information Systems 2 Auditing Software.pdf ORDINANCE AUTHORIZING AND DIRECTING THE CITY AUDITOR TO ENTER INTO CONTRACT WITH SOFTWARE SOLUTIONS (SSI) AND RIGHT STUFF SOFTWARE ON BEHALF OF THE CITY OF MARION FOR THE REPLACEMENT OF THE CITY’S COMPUTER SOFTWARE SYSTEM AND RELATED SOFTWARE AND DECLARING AN EMERGENCY INCLUDING PURSUANT TO ORC 735.051.”
“Marion City Council Information Systems Committee 08/17/2026 at 6:33 PM CALL TO ORDER R. Smith, Rollins, Clark.”
This emergency push is happening while the city faces four consecutive years of unfinished audits, severe IRS penalties, denied federal appeals, active claims against the city’s bond, and a looming credit rating downgrade.
The cause of Marion’s current crisis is clear:
The vast majority of this financial destruction, including the unreconciled books, is the direct, proven result of the software and governance failures meticulously documented throughout the Silent Sabotage series and across Marion Watch platforms.
The IRS penalties did not happen in a vacuum; they were the direct consequence of unshared and undocumented manual workarounds forced by software safety module failures and widespread misconfigurations.
Relying on manual workarounds in an enterprise system of this scale for an extended period is a grave breach of global I.T. standards that caused catastrophic misalignments in payroll, benefits, and tax tracking.
Furthermore, the unfinished audits and unreconcilable ledgers are the direct, proven result of an enterprise system that could not handle hybrid cash-accrual accounting natively, combined with an IT environment where software safety controls were suppressed, and users across various departments possessed unimpeded administrative access to override budget balances at will.
Instead of fixing the root governance failure, is the administration attempting to simply replace the ledger while the ledger itself remains unreconciled, unverified, and dangerously compromised?
The core lesson remains:
Marion has already lived through the consequences of rushing a system installation.
The New World system was rushed when it was installed.
Is the Software Solutions system now being rushed in the exact same way?
Marion Watch is heavily involved in monitoring this transition. To prevent history from repeating itself, we have directly contacted Information Systems Committee Chairman Ralph Smith to ensure these critical concerns are officially noted on the record.
We trust Chairman Smith’s technical oversight. As a former U.S. Army IT professional with high-level security clearance, who previously owned a local computer store and worked stateside in coding and software development, he understands that the rules governing safe, compliant IT processes are non-negotiable. Ralph has been a vocal supporter of a full forensic IT audit.
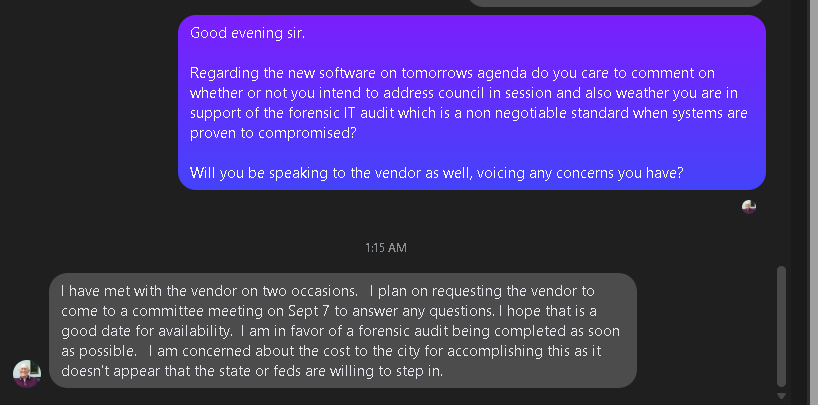
With that technical reality in mind, we must view the current rush as a massive liability. Will the catastrophic cycle documented in Silent Sabotage be locked into place for another generation?
THE NEW WORLD INSTALLATION WAS RUSHED — AND IT CREATED FIFTEEN YEARS OF DAMAGE
Silent Sabotage documented that the New World ERP system was never properly installed from day one in 2009.
The city bypassed mandatory configuration steps.
The city ignored warnings from IT professionals.
The city allowed unauthorized staff to manipulate permissions directly with the vendor.
Software safety controls were never activated.
Segregation of duties was never enforced.
The system was never secured.
Most critically, the software was never configured to handle the city’s fundamental accounting reality: hybrid cash-accrual processing.
Because the software could not balance modified cash basis operations against statutory accrual mandates, the general ledger fractured.
Instead of fixing the configuration, staff turned to unshared and undocumented manual workarounds to force numbers to match.
Relying on manual workarounds in this type of system for a long period of time is a grave breach of global I.T. standards.
And one failure stands above all others:
The New World system operated with unimpeded administrative access, leaving budget and ledger overrides wide open across departments—a catastrophic vulnerability officially proven in the corrective action plan of the released 2021 Ohio Auditor of State (AOS) audit.
According to the city’s own official response in that state audit, permissions to override budgets were openly available to users across the entire New World system and were not rescinded until October 27, 2025.
This reality raises critical questions for current leadership:
- Did users with elevated access alter financial records without detection because audit logs were suppressed?
- How many departments routinely bypassed internal controls by using widespread budget override permissions?
- Because there is still no centralized point of control for permission changes to this day, how often are individuals currently bypassing City IT to contact the software vendor directly and alter settings or elevate privileges?
- How many unverified balance adjustments were executed that left zero digital audit trail?
This single failure—unimpeded administrative access granted coupled with suppressed software safety controls—is the root cause of Marion’s financial collapse:
- It enabled unauthorized data manipulation across departments.
- It drove the reliance on unshared and undocumented software workarounds.
- It produced unexplained record gaps and disappearing transactions.
- It allowed corrupted balances to compound across multiple fiscal cycles.
- It allowed elevated administrative credentials to remain active long after former employees left public office.
- It degraded the city’s financial baseline year after year.
The collapse Marion is living through today did not begin with basic accounting errors. It began with a rushed, unchecked installation that left the city’s financial vault wide open.
THE SILENT SABOTAGE DOSSIER: A RUNDOWN OF SYSTEMIC COLLAPSE
Over years of investigative reporting, Marion Watch has uncovered a systemic, 15-year breakdown of technical governance and internal control mechanisms across Marion’s municipal software:
- Systemic Suppression of Software Safety Controls: An estimated 80% of the native software safety controls within the city’s enterprise software were never configured or activated, eliminating the digital paper trail required to verify who created, edited, or deleted financial transactions.
- The Hybrid Cash-Accrual Failure: The ERP software suffered catastrophic breakdowns attempting to process hybrid cash-accrual accounting, causing unrecorded ledger drift, unbalancing fund accounts, and creating massive multi-year reconciliation failures.
- Unchecked Vendor Backdoors: A documented practice where individual department personnel completely bypassed City IT, directly contacting software vendors to request administrative changes, permission overrides, and custom database scripts with zero written tickets or oversight.
- The Violation of Least Privilege & Administrative Overreach: Multiple individuals possessed access to the system with zero business need. Marion Watch has released screenshots dated 2001 proving that at least one former deputy auditor retained full administrative access even after transitioning to an appointed position outside the office.
This represents a multi-tiered collapse of global I.T. and financial standards:
- The Post-Transition Breach: Allowing an appointed official outside the finance department to retain full access to the city’s financial software allows them to alter records, view sensitive data, and bypass controls with zero operational justification or oversight.
- The Deputy Auditor Breach: Even while this official was serving as deputy auditor, holding full IT administrative rights was a severe violation of the “Segregation of Duties.” The individual responsible for processing daily financial transactions cannot concurrently hold the master IT keys to alter the software’s rules, delete logs, or bypass the very internal controls meant to govern those transactions.
- The Elected Auditor Breach: Global financial and I.T. standards strictly dictate that even the elected Auditor must never hold full IT administrative access. There must be an impenetrable wall between the financial officer who manages the ledger and the IT administrator who manages the software’s security architecture. If the Auditor acts as their own IT administrator, the internal control environment effectively ceases to exist—they possess the unchecked power to alter permissions, disable safety modules, and rewrite the ledger without leaving a digital trace.
- The Crisis of Unshared and Undocumented Workarounds: Due to failed software safety modules and misconfigurations, staff routinely deployed unshared and undocumented manual workarounds and spreadsheet overrides. Relying on manual workarounds in this type of system for a long period of time is a grave breach of global I.T. standards and directly poisoned the integrity of the core ledger.
- The Payroll and Tax Penalty Cascade: Total misalignment between internal timekeeping, benefits tracking, and software reporting led to inaccurate federal filings, resulting in compounding IRS penalties, state pension fund defaults, and severe financial liabilities.
- Independent Confirmation of Structural Breakdown: Independent financial forensic audit evaluations conducted by Veritas confirmed critical security vulnerabilities, structural control bypasses, corrupt data, ghost data, and an unmonitored technical environment across city systems.
- The Public Records Blackout: City officials have repeatedly stonewalled and blanket-denied statutory public records requests for user permission matrices, module configuration inventories, and vendor helpdesk logs, actively concealing the true scope of the compromise. There are well-established state and federal high court precedents that show they are in violation of cases ruled by the highest courts in Ohio and in the nation.
Is this the operational wreckage that the administration is now trying to sweep into a brand-new software system without an independent investigation?
THE SOFTWARE SOLUTIONS MIGRATION IS BEING RUSHED IN THE SAME WAY
The emergency ordinance is being used to accelerate a software migration that has no forensic baseline, no verified ledger, no validated balances, and no structural controls. Is the administration attempting to migrate corrupted data into a new platform under emergency authority?
The same warning signs that preceded the New World collapse are flashing red right now, serving as urgent warnings formatted as questions this administration must answer:
- Is the city bypassing forensic verification?
- Is the city bypassing proper module configuration?
- Is the city bypassing centralized IT control?
- Is the city bypassing software safety control mandates?
- Is the city bypassing permissions governance?
- Is the city bypassing internal control safeguards?
- Is the city bypassing statutory accountability?
- Is the city bypassing public transparency?
And most critically, we must ask the loudest warning question of all:
Is the city attempting to install a new system while budget overrides and vendor backdoors still exist?
- Employees and officials still contact vendors directly.
- There still no mandatory permissions matrix defining who holds elevated overrides.
- There still no enforced IT ticketing system.
- Is there still no immutable audit trail?
- Is there still no centralized IT command?
- Is there still no enforced segregation of duties?
- Is there still no independent forensic oversight?
The New World disaster was not an accident. It was the result of rushing.
Will the Software Solutions disaster be the direct result of rushing as well?
THE LEGACY SYSTEM IS COMPROMISED AND CANNOT BE MIGRATED WITHOUT FORENSIC OVERSIGHT
The New World database is a compromised environment.
It has suffered from unmonitored permission bypasses by users across the network, unshared and undocumented workarounds due to software safety module misconfigurations, unexplained record gaps, disabled software safety controls, and years of manual budget adjustments that were never subjected to an internal control review.
The danger is simple: Garbage In, Garbage Out.
If Marion migrates this data without an independent forensic audit, will fifteen years of corruption be permanently baked into the Software Solutions platform?
Furthermore, this data corruption creates a latent time-bomb.
Corrupted data imported during a rushed migration will not be immediately apparent on day one. It will lay dormant inside the new system until year-end reconciliations, future state audits, or debt filings fail, throwing Marion right back into an inescapable financial black hole.
Federal standards and leading cybersecurity frameworks strictly mandate independent forensic intervention when an enterprise system suffers an integrity breakdown.
While this audit does not necessarily have to halt all progress, it is an absolute requirement that it be conducted prior to or in parallel with the transition:
- The Government Accountability Office (GAO): Federal modernization standards dictate that legacy data conversion must be rigorously managed and validated prior to or alongside migration to prevent importing material weaknesses and compromised system baselines into new environments.
- National Institute of Standards and Technology (NIST SP 800-171): Mandates that organizations maintain comprehensive audit records and execute rigorous data integrity validations to protect systems against undetected manipulation as data moves between environments.
- Information Systems Audit and Control Association (ISACA ITAF): Establishes that enterprise software transitions require strict baseline assessment controls and independent audit verification to ensure system reliability and eliminate opportunities for fraud.
Marion’s system did not suffer an accidental glitch. It suffered a fifteen-year collapse of basic IT governance driven by a grave breach of global I.T. standards.
Why hasn’t the administration commissioned a forensic audit?
Why hasn’t the administration required forensic oversight before or alongside the migration?
Why hasn’t the administration produced any technical proof that the legacy data is trustworthy?
Is the administration simply attempting to force a compromised database into a new system under emergency authority?
THE FINANCE COMMITTEE CONTEXT PROVES THE SYSTEM IS COLLAPSED
The Finance Committee agenda places the software contract directly beneath an unprecedented list of active municipal financial disasters:
“Item 1. Audits — 2022, 2023, 2024, and 2025 (Auditor) –> S&P Credit Watch/Bond Rating”
“Status of denied appeals filed by Auditor’s Office with IRS”
“Status of Police and Fire Pension Fund claim against bond”
“Status of IRS claim against bond (Ordinance 2024-088)”
These agenda items confirm that Marion is not merely behind on paperwork. The city is in a state of Fiscal Emergency, entangled in active conflict with federal revenue agencies, state pension authorities, and Wall Street credit rating agencies.
Is the city attempting to migrate data that has already triggered federal penalties, insurance bond claims, and state audit escalations? Migrating this corrupted data into a new database will not resolve these crises; it will permanently conceal the origin of the failure while perpetuating the damage.
THE TECHNICAL REALITY: VENDOR ASSURANCES ARE NOT FORENSIC AUDITS
Software Solutions Inc. explicitly acknowledges in its own publication, What is Data Conversion and Why Does it Matter? (March 18, 2024), that data migration requires a comprehensive “Data Cleansing” phase to eliminate errors, inconsistencies, and duplicates before import. Furthermore, SSI notes in What to Expect from an ERP Partner (July 20, 2026) that migration errors negatively impact audits, reconciliations, and executive decisions “long after launch.”
These mandatory cleansing and validation steps cannot be executed on a database where software safety controls were never activated, records have changed without explanation, and unrecorded, unshared workarounds were the standard operating procedure for users across the city.
- Does the vendor have forensic IT experts who will be vetting this data?
- Can the vendor validate data that the city cannot explain?
- Can the vendor cleanse data that the city cannot reconcile?
- Can the vendor guarantee accuracy when the baseline is fundamentally compromised by a decade of global I.T. standard breaches?
- Will the vendor assume legal liability for fifteen years of unverified ledger drift?
- Can the vendor protect the taxpayers from the consequences of a compromised legacy system?
Independent industry data from Gartner and the Bloor Group confirms that over 83% of data migrations fail, exceed their budgets, or run significantly over schedule due to legacy data issues. Bypassing forensic oversight for a municipality under a state of fiscal emergency defies basic professional standards.
THE GOVERNANCE FAILURE REMAINS UNCHANGED
Marion still does not have a centralized point of control for permission changes. Employees across multiple departments still contact software vendors directly. There is still no written permissions matrix. There is still no IT ticketing system.
This is not a software problem. This is a governance collapse.
Will migrating to Software Solutions and Right Stuff Software without fixing administrative governance guarantee that the exact same failures corrupt the new platform?
The city must adopt binding legislation requiring centralized IT control, mandatory ticketing, immutable software safety controls, and strict segregation of duties before a single piece of software is configured. Without these controls, the new system will fail just as catastrophically as New World.
WHAT COUNCIL MUST DEMAND BEFORE ANY VOTE
Members of Marion City Council must reject salesman rhetoric and demand technical, legally binding answers before approving any contract:
- A Full Independent Forensic IT Audit: An external, certified forensic firm (holding GCFA or CFCE credentials) must be contracted to audit, cleanse, and oversee the data transfer. This audit can be conducted in parallel with the transition, but it is an absolute requirement that must be actively executed alongside the migration.
- A Verified Financial Baseline: Full mathematical and forensic reconciliation of all accounts, funds, and hybrid cash-accrual ledgers before data mapping begins.
- An Enforced Permissions Matrix: A hard-coded, role-based access architecture with absolute segregation of duties, ending all direct-to-vendor access and unauthorized budget overrides.
- A Mandatory IT Ticketing Infrastructure: Binding policy that prohibits any configuration, access grant, or software modification without an approved, written IT ticket.
- Immutable Audit Logging: Verification that software safety controls within both Software Solutions and Right Stuff Software are permanently enabled, restricted from administrative tampering, and archived externally.
- Clear Vendor Liability: Contractual terms holding the vendor liable for data conversion failures and migration-induced reporting errors.
- Strip the Emergency Clause for Parallel Oversight: Stripping the emergency clause from the ordinance so the legislation is firmly bound to an independent forensic IT audit. The city cannot authorize a blind rush; forensic oversight must operate alongside the transition to verify the data before the new system goes live.
Moving Forward
Marion is standing directly at the edge of a second technological and financial collapse. Is the administration attempting to push an emergency migration of a broken system into a new platform to create the illusion of progress?
If so, this is not modernization. This is replication.
This is not a clean slate. This is the transfer of corruption.
This is not a solution.
This is a guarantee that the next generation of Marion taxpayers will pay for the unresolved failures of the last fifteen years.
The damage inflicted upon the citizenry by these systemic breakdowns is immeasurable. Accountability must finally be realized. If Marion City Council approves this migration without mandating an independent forensic IT audit alongside it, the financial black hole will it become worse.